How much does penetration testing cost for a small business?
At Summit Cyber Group, penetration testing for a small business starts at $5,000 for a one-time Security Baseline Engagement; final cost depends on scope and exposure. For ongoing coverage, the Security Progress Program starts at $3,000 per month and includes quarterly targeted testing, continuous dark web monitoring, remediation validation, and a monthly advisory call.
What is a vCISO, and does a small business need one?
A vCISO (virtual or fractional Chief Information Security Officer) is a senior security leader who runs your security program part-time, for a fraction of the cost of a full-time hire. Summit's vCISO service covers a 12-month security roadmap, board and executive reporting, policies, vendor risk, incident response planning, security questionnaires and customer audits, and an annual penetration test. It suits businesses that need security leadership and accountability but not a full-time executive.
Which compliance frameworks do you help with?
Summit Cyber Group supports SOC 2, ISO 27001, HIPAA, PCI DSS, NIST CSF, and CMMC. We run gap assessments and readiness reviews, build your risk register, guide control implementation, and help collect evidence and support you through the audit.
What is a Free Exposure Snapshot?
A Free Exposure Snapshot is a lightweight assessment of your external exposure signals, common misconfigurations, and credential exposure indicators. It gives leadership a quick, structured view of risk and where to focus first.
Do small businesses really need cybersecurity testing?
Yes. Small and mid-sized businesses are frequently targeted because their security resources are limited. Structured offensive testing identifies and prioritizes risk before it becomes an incident.
Do you work with companies that don't have dedicated security staff?
Yes. Summit Cyber Group is built for SMBs with limited IT and security staffing. We deliver structured, prioritized work your team can act on without adding a full-time security hire.
Is your penetration testing automated or done by people?
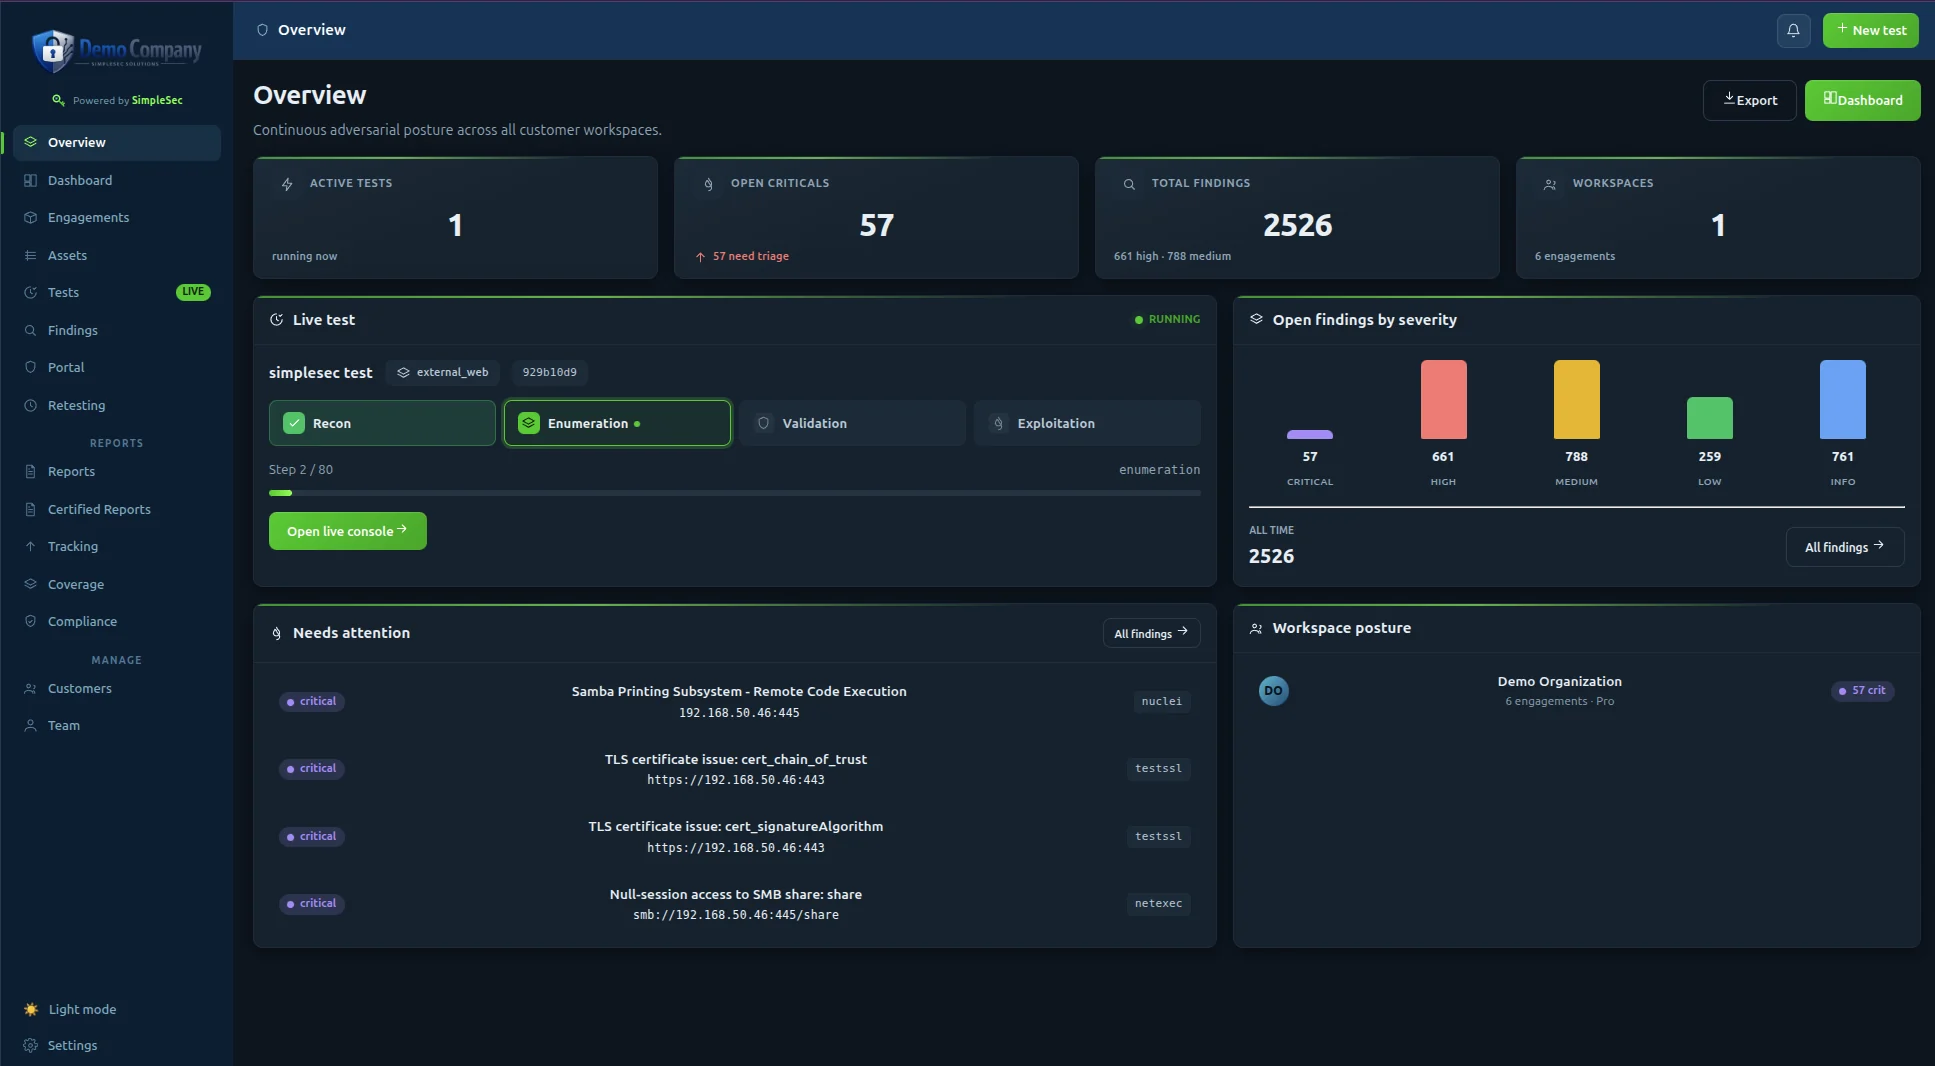
Both, depending on what each client needs. Every Summit penetration test is scoped, run, and validated by a human pentester on our team. Where it helps, we also use SimpleSec, our own AI-orchestrated platform, to handle reconnaissance and enumeration at scale — so our testers spend their time on exploitation and on chaining vulnerabilities together the way real attackers do. Clients who subscribe to SimpleSec can also run automated, AI-orchestrated tests on demand, which our team can review and certify.
Who will I actually work with?
You work directly with the security professional performing the engagement — no subcontractors, no account managers, and no third-party markup.
Where is Summit Cyber Group based?
Summit Cyber Group, LLC is a US-based cybersecurity firm headquartered in Colorado, with penetration testers in other states across the US. You work directly with the security professional performing your engagement — no subcontractors, no account managers, and no third-party markup.
Who founded Summit Cyber Group?
Summit Cyber Group, LLC was founded in 2025 by co-founders Tricia Bohm and Rick Bohm. The company is headquartered in Colorado and is not affiliated with Summit Cyber Group of Perth, Australia.
What certifications does the Summit Cyber Group team hold?
Summit Cyber Group's vCISO and penetration testing team holds CISSP, CCISO, OSCP, CPTS, CRTO, CEH, BSCP, CWES, OSWP, CFCE, and CIAM certifications — covering security leadership (CISSP, CCISO), hands-on penetration testing and red teaming (OSCP, CPTS, CRTO, CEH), web application and wireless testing (BSCP, CWES, OSWP), digital forensics (CFCE), and identity and access management (CIAM).